Microsoft Paint flaw could let attackers run code over a network
★ Add us as a preferred source on GoogleTL;DR
Microsoft says a vulnerability in Paint, identified as CVE-2026-83844, could allow remote code execution via a network packet, and the fix is delivered through the Microsoft Store rather than the standard Windows update.
Microsoft disclosed a security flaw in Paint on October 13, 2026, that could allow an attacker to run code on a PC over a network. Microsoft rated the CVE-2026-83844 vulnerability with a severity score of 8.1 out of 10 and classified it as "Important." The company says an attacker could exploit the vulnerability by transmitting a custom data packet to a vulnerable component without requiring user authentication.
According to the software maker, exploiting the security issue is challenging, and available data indicates no active attacks in the wild. A fix is included in Paint version 11.2609.401.0 and newer. Because the patch is distributed through the Microsoft Store, installing the October 2026 Windows update does not guarantee the app is updated. Sources note that some users remained on version 11.2603.251.0 even with automatic Store updates enabled.
More on Microsoft
Via PCWorld ↗ · Also from VGTimes ↗
Spot a mistake? Tell usEarlier coverage
Quick read
Osvaldo Doederlein reports that Microsoft's new DXR API features, specifically Clustered Geometry, increased ray tracing performance from 1.4fps to 310fps on a GeForce RTX 5080.
Quick read
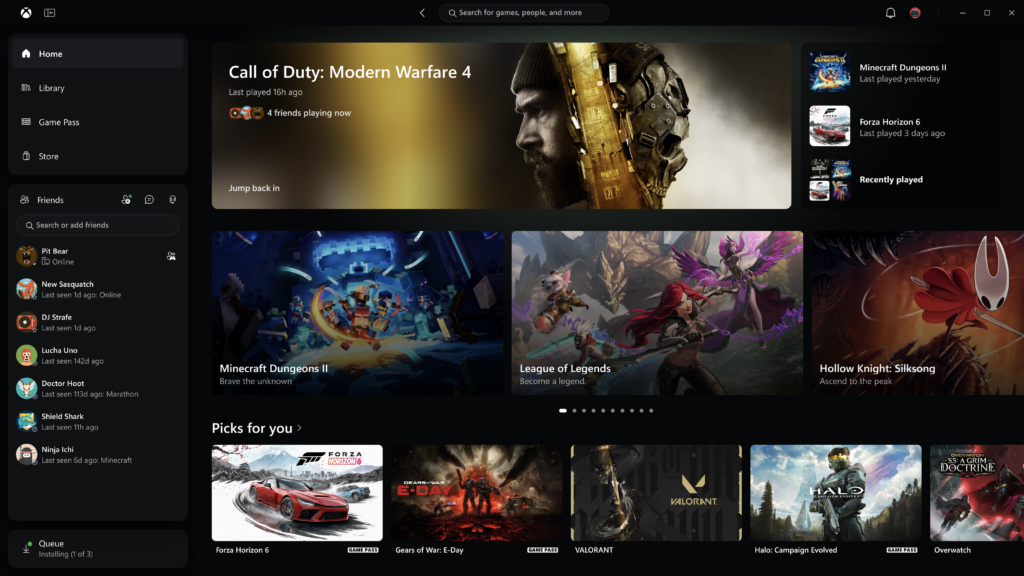
Microsoft released an update for Xbox Insiders on November 5, 2026, that speeds up the Xbox PC app and refreshes the web and cloud gaming experiences.
Quick read
Microsoft's DirectX 12 Agility SDK 1.722 Preview and AMD's November 3 driver update bring Clustered Geometry support to RDNA 4 graphics cards. Independent testing shows dramatic memory and frame rate gains in synthetic workloads.
Quick read
A leaked Microsoft slide outlines an upcoming hardware roadmap that categorizes Windows personal computers according to system memory tiers.